GitDash
DocsAPI playgroundGitHub
Open GitDash
GitDash Docsv4.7.1
GitHub API playground
  • Introduction
  • Quick start
  • Deployment
  • Configuration
  • Auth modes
  • Access control
  • Caching & rate limits
  • Security model
  • Data sources
  • Feature overview
  • Repositories
  • Repository · Overview
  • Repository · Workflows
  • Repository · Pull requests
  • Repository · Team
  • Repository · Issues
  • Repository · Security
  • Repository · Audit trail
  • Workflow detail
  • Alerts
  • Team insights
  • Contributor & 1:1 prep
  • Cost
  • Reports
  • Org overview & health
  • Settings
  • AI insights
  • Metrics Reference
  • DORA 4 Keys
  • PR Cycle Time
  • PR Lifecycle Health
  • Workflow Overview
  • Performance Tab
  • Reliability Tab
  • Team & People
  • CI & Alert Metrics
  • API Reference
  • FAQ & Troubleshooting
  • Contributing
  • Release Notes
  • Data & privacy
GitHub RepositoryReport an Issue
GitDash Docs

Repository · Security

/repos/[owner]/[repo]/security
DependabotCode scanningSecret scanningWorkflow analysis
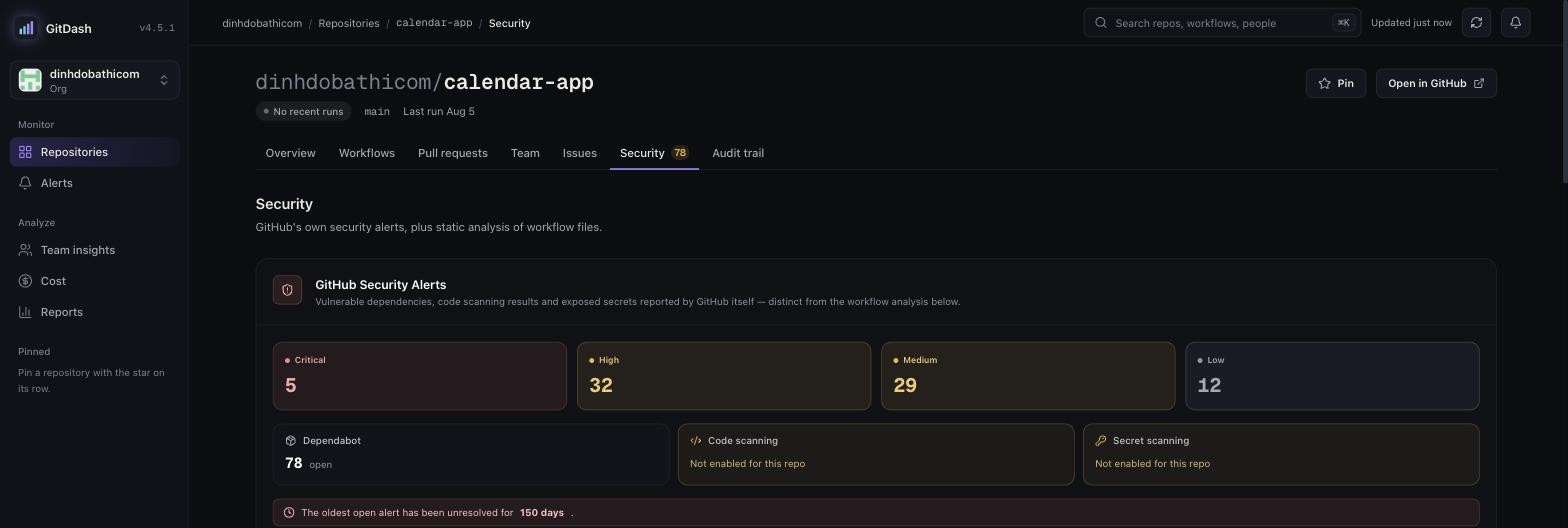
Repository security
SectionWhat it shows
GitHub security alertsDependabot, code-scanning and secret-scanning alerts with counts, oldest open and time to fix. Each source reports its own status: a feature switched off on the repository shows as “Not enabled”, a token without access as a permission warning — never as zero alerts.
Workflow static analysisChecks workflow files for risky patterns — pull_request_target triggers, secrets echoed to logs, passed as arguments or written to outputs, unquoted dispatch inputs, actions pinned to a branch, missing timeouts or permissions — grouped by severity. Needs the securityScan feature.
A classic token with repo reads all three alert sources; fine-grained tokens need the matching read permissions for Dependabot, code scanning and secret scanning.
PreviousRepository · IssuesNextRepository · Audit trail

GitDash v4.7.1 — GitHub Actions Dashboard

Open source on GitHubData & privacyReport an issue